
London, UK – [Date of Publication] – The National Health Service (NHS) has embarked on a pivotal mission to achieve comprehensive cyber resilience across its vast network of healthcare organisations by the year 2030. This ambitious undertaking, requiring a sophisticated blend of cutting-edge technology, specialized expertise, and unprecedented collaboration between the public and private sectors, marks a critical juncture in safeguarding the nation’s health data and ensuring the uninterrupted delivery of care. At the forefront of this transformative initiative is the unveiling of the next generation of the NHS Secure Boundary programme, a testament to the evolving threat landscape and the unwavering commitment to fortifying digital infrastructure.
The Imperative for Enhanced Cyber Resilience
In an era defined by rapid digital transformation, the NHS finds itself operating within an increasingly intricate ecosystem. The growing reliance on digital systems, the expansion of complex supply chains, the ever-present and evolving nature of cyber threats, and the disruptive influence of emerging technologies like Artificial Intelligence (AI) collectively reshape the operational landscape. This dynamic environment amplifies the urgency for robust and secure digital infrastructure, making resilient cybersecurity a paramount concern.
The financial repercussions of cyber incidents within the healthcare sector are starkly illustrated by IBM’s authoritative Cost of a Data Breach Report. Consistently ranking among the most impacted sectors globally, healthcare organisations face significant financial burdens when their digital defenses are compromised. This reality underscores the critical need for a proactive, long-term strategy to bolster cyber resilience across all essential public services.
A Strategic Partnership for a Secure Future
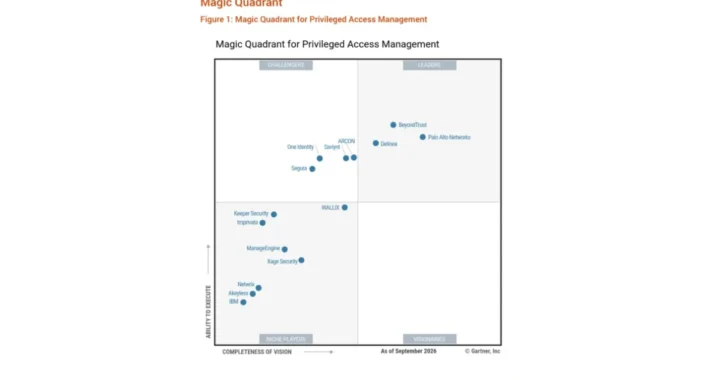
To navigate this complex terrain and achieve its ambitious 2030 goal, the NHS is forging strategic alliances. A key partnership has been established with Palo Alto Networks, a global leader in cybersecurity, and IBM Consulting, a powerhouse in technology services and strategic guidance. This collaboration is designed to accelerate the NHS’s journey towards enhanced cyber resilience.
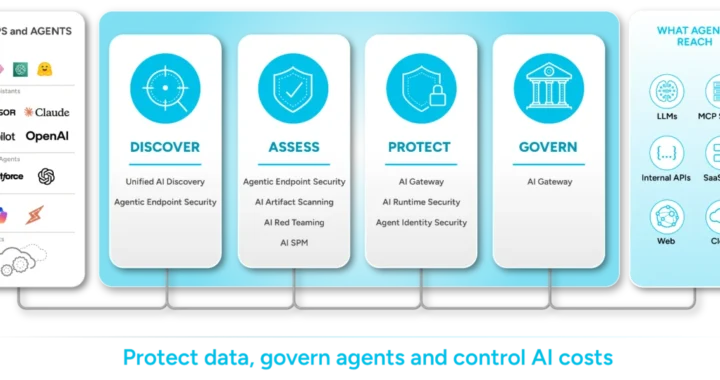
Under this partnership, Palo Alto Networks will deploy its advanced cloud-based perimeter technology, offering a sophisticated layer of defense against evolving cyber threats. Complementing this technological prowess, IBM Consulting will provide invaluable specialist guidance, comprehensive implementation support, and tailored onboarding services specifically designed for NHS organisations. This integrated approach ensures that healthcare providers are not only equipped with state-of-the-art security solutions but also empowered with the knowledge and support to effectively deploy and manage them.
Introducing the Next Generation of the NHS Secure Boundary Programme
Central to the NHS’s strategy is the evolution of its Secure Boundary programme. The next iteration of this vital initiative will leverage Palo Alto Networks’ next-generation, cloud-based security solutions. This programme is meticulously crafted to significantly strengthen cyber resilience across the entirety of the UK’s health and social care organisations, thereby supporting the safe, reliable, and continuous delivery of essential services.
The Secure Boundary programme is engineered to manage an enormous digital footprint. It encompasses a network spanning over 1.5 million NHS staff, more than 200 NHS trusts, upwards of 55,000 organisations entrusted with handling sensitive health data, and approximately 2 million devices currently under national cyber monitoring. This nationally integrated and centrally funded service champions a "Defend as One" philosophy. This approach fosters a collaborative security posture, enabling all participating organisations to benefit from shared protection and collective intelligence, while crucially retaining the autonomy and flexibility to manage their local security needs.
Pillars of Support for NHS Organisations
The revamped Secure Boundary service is poised to provide multifaceted support to NHS organisations, addressing their diverse and evolving security requirements. Key areas of support include:
- Enhanced Threat Detection and Prevention: The deployment of advanced, cloud-native security solutions will enable real-time monitoring and analysis of network traffic, identifying and neutralizing threats before they can impact critical systems. This proactive approach moves beyond traditional perimeter defenses to offer a more dynamic and intelligent security posture.
- Cloud Security Posture Management: As NHS organisations increasingly adopt cloud technologies, ensuring their secure configuration and ongoing compliance is paramount. The Secure Boundary programme will offer robust tools and expertise to manage cloud security postures effectively, minimizing vulnerabilities.
- Data Protection and Privacy: Safeguarding sensitive patient data is a core responsibility. The programme will implement stringent measures to protect data at rest and in transit, ensuring compliance with privacy regulations and maintaining patient confidentiality.
- Incident Response and Recovery: In the unfortunate event of a cyber incident, rapid and effective response is crucial to mitigate damage and restore services. The Secure Boundary programme will integrate enhanced incident response capabilities, streamlining recovery processes and minimizing downtime.
- Supply Chain Security: The interconnected nature of modern healthcare means that vulnerabilities in the supply chain can pose significant risks. The programme will extend its protective umbrella to address security across the extended digital supply chain, identifying and mitigating risks associated with third-party vendors and partners.
- Scalability and Flexibility: Recognizing the diverse needs of NHS organisations, from large acute trusts to smaller community services, the Secure Boundary programme is designed to be scalable and adaptable. It offers a flexible framework that can be tailored to meet specific local requirements and operational demands, while still adhering to national security standards.
- Centralized Visibility and Management: The programme aims to provide a consolidated view of the security landscape across the NHS, enabling better situational awareness and more effective strategic decision-making. This centralized approach facilitates the identification of systemic risks and the allocation of resources where they are most needed.
- Empowering Local Control: While promoting a "Defend as One" ethos, the Secure Boundary programme is carefully designed to empower local NHS organisations. They will retain the ability to manage their specific security configurations, access control policies, and incident response protocols, ensuring that national security measures do not impede local operational agility.
- Continuous Improvement and Innovation: The threat landscape is in constant flux. The Secure Boundary programme will be underpinned by a commitment to continuous improvement, incorporating the latest threat intelligence and cybersecurity innovations to stay ahead of emerging risks. This includes leveraging AI and machine learning for advanced threat detection and response.
- Cost-Effectiveness and Resource Optimization: By providing a centrally funded and integrated security service, the programme aims to achieve economies of scale, reduce duplication of effort across different trusts, and optimize the use of valuable cybersecurity resources, allowing individual organisations to focus on their core mission of patient care.
A Chronology of Transformation
The journey towards enhanced cyber resilience within the NHS is a multi-faceted and ongoing process. While specific timelines for individual technological deployments are often proprietary, the strategic commitment to achieving cyber resilience by 2030 represents a clear roadmap. This ambition builds upon years of increasing recognition of the cyber threat to healthcare.
Early efforts focused on establishing basic cybersecurity hygiene and awareness programs. As threats became more sophisticated, the focus shifted towards more robust network security, including firewalls and intrusion detection systems. The development of the initial Secure Boundary programme marked a significant step towards a more coordinated and national approach. The current iteration, powered by advanced cloud-based solutions from Palo Alto Networks and strategic guidance from IBM, signifies a leap forward in sophistication and comprehensive coverage. This evolution reflects a proactive and adaptive strategy, recognizing that cybersecurity is not a static achievement but a continuous process of adaptation and improvement.
Supporting Data: The Growing Threat Landscape
The urgency behind the NHS’s cyber resilience drive is substantiated by a wealth of data highlighting the escalating threat to healthcare systems globally.
- IBM’s Cost of a Data Breach Report: As previously mentioned, this report consistently identifies healthcare as one of the most targeted and financially impacted sectors. The average cost of a data breach in healthcare continues to rise, driven by the sensitive nature of patient data and the critical operational demands of healthcare services. The report often highlights factors such as the length of time to identify and contain breaches, the impact of regulatory fines, and the cost of business disruption as key drivers of these escalating costs.
- Ransomware Attacks: The healthcare sector remains a prime target for ransomware attacks. These malicious attacks encrypt vital data and systems, demanding significant ransoms for their release. The impact on patient care can be catastrophic, leading to cancelled appointments, delayed treatments, and compromised medical procedures. Data from cybersecurity firms frequently indicates a disproportionate number of ransomware attacks targeting hospitals and health systems compared to other industries.
- The Value of Health Data: Protected Health Information (PHI) is highly valuable on the black market, making healthcare organisations attractive targets for cybercriminals seeking to steal personal and financial data for identity theft, fraud, and other illicit activities.
- Increasing Sophistication of Attacks: Cyber adversaries are constantly refining their techniques, employing sophisticated social engineering tactics, advanced malware, and zero-day exploits to bypass traditional security measures. This necessitates the adoption of more advanced, intelligent, and adaptive security solutions.
- Interconnectedness and Vulnerabilities: The increasing adoption of interconnected medical devices (IoT) and the reliance on cloud services introduce new attack vectors. Each connected device and each cloud service represents a potential point of entry for attackers if not adequately secured.
Official Responses and the "Defend as One" Philosophy
The commitment to cyber resilience is not merely a technological endeavor; it is also a strategic imperative articulated by key figures within the NHS and government. The "Defend as One" philosophy is central to this strategic vision. It signifies a paradigm shift from individual organisations fending for themselves to a collective, unified defense posture.
This approach emphasizes:
- Shared Intelligence: By pooling threat intelligence and insights, the NHS can gain a more comprehensive understanding of emerging threats and develop more effective countermeasures.
- Coordinated Response: In the event of a significant cyber incident, a unified response mechanism ensures that resources are deployed efficiently and effectively across the entire network.
- Best Practice Sharing: The "Defend as One" model encourages the dissemination of best practices in cybersecurity, enabling all organisations to learn from the experiences and successes of others.
- Leveraging Collective Strength: By working together, the NHS can achieve a level of cybersecurity that would be unattainable for individual organisations acting in isolation.
This collaborative spirit is a cornerstone of the partnership with Palo Alto Networks and IBM Consulting, ensuring that the technological solutions are embedded within a broader strategic framework for collective security.
Implications for the Future of Healthcare
The successful implementation of the NHS’s cyber resilience goals and the evolution of the Secure Boundary programme carry profound implications for the future of healthcare in the UK:
- Uninterrupted Patient Care: The most significant implication is the enhanced ability to ensure the continuous and safe delivery of healthcare services. By minimizing the risk of cyberattacks disrupting operations, patients can rely on timely appointments, access to their medical records, and the uninterrupted functioning of critical medical equipment.
- Safeguarding Sensitive Information: The program’s robust security measures will provide greater assurance that sensitive patient data remains confidential and protected from unauthorized access or breaches, thereby preserving patient trust and privacy.
- Enabling Digital Innovation: A secure digital infrastructure is the bedrock upon which future innovation can be built. With enhanced cyber resilience, the NHS can more confidently embrace new technologies, such as AI-powered diagnostics, remote patient monitoring, and advanced data analytics, to improve patient outcomes and operational efficiency.
- Economic Benefits: By reducing the financial impact of cyber incidents, the NHS can redirect resources that would otherwise be spent on breach recovery, regulatory fines, and legal costs towards frontline patient care and service improvement.
- Strengthening National Security: The NHS is a critical national infrastructure. Its cyber resilience is intrinsically linked to national security, ensuring that the country can effectively respond to threats that could impact public health and well-being.
- A Model for Other Sectors: The NHS’s ambitious cyber resilience program, with its focus on public-private partnerships and a "Defend as One" approach, could serve as a valuable model for other critical sectors facing similar cybersecurity challenges.
In conclusion, the NHS’s commitment to achieving cyber resilience by 2030, bolstered by the next generation of the Secure Boundary programme and strategic partnerships with industry leaders like Palo Alto Networks and IBM Consulting, represents a significant and necessary step forward. This initiative not only addresses the immediate and evolving threats to healthcare data and services but also lays a robust foundation for a secure, innovative, and resilient digital future for the UK’s health and social care system, ultimately benefiting millions of patients across the nation.
For further information on the Secure Boundary programme and how it can support your organisation, please contact [email protected].
Forward-Looking Statements:
This article contains forward-looking statements that involve risks, uncertainties, and assumptions. These statements relate to the anticipated benefits, impact, performance, or potential benefits, impact, or performance of products, technologies, or future products and technologies. It is important to note that these forward-looking statements are not guarantees of future performance. A significant number of factors could cause actual results to differ materially from those expressed in these statements. Specific risks and uncertainties that could affect results and performance are detailed in the most recent Annual Report on Form 10-K, Quarterly Report on Form 10-Q, and other filings with the U.S. Securities and Exchange Commission, available on the respective websites. All forward-looking statements herein are based on information available as of the date of this article, and no obligation is assumed to update these statements to reflect events or circumstances occurring after the date of publication.