
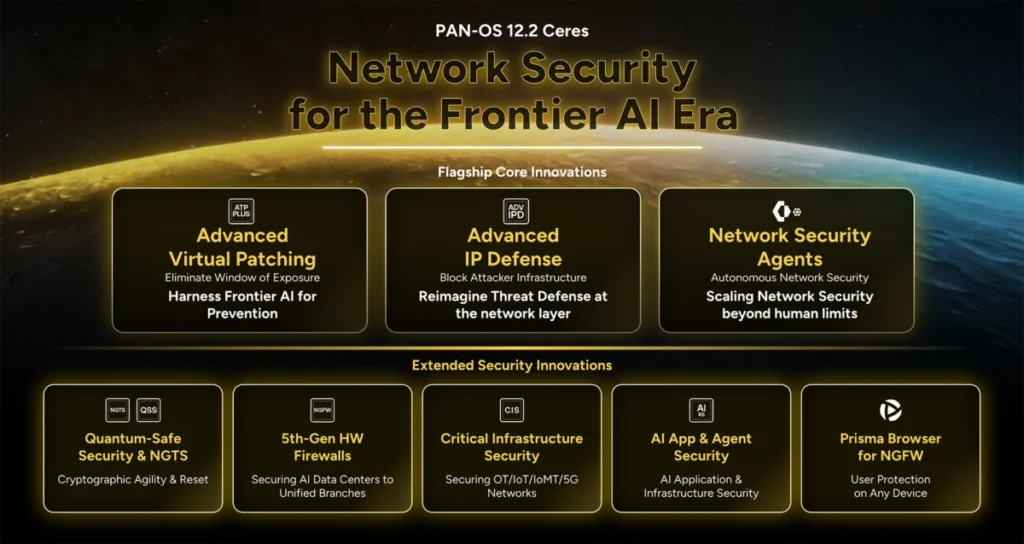
SANTA CLARA, CA – [Insert Date] – In a dramatic escalation of the cyber arms race, Palo Alto Networks today announced PAN-OS 12.2 Ceres, a groundbreaking release poised to redefine enterprise resilience in the face of rapidly evolving threats. The new operating system introduces over 55 innovations, including three flagship capabilities – Frontier Virtual Patching, Advanced IP Defense, and Network Security Agents – designed to equip Chief Information Officers (CIOs) and Chief Information Security Officers (CISOs) with the tools to build a cybersecurity architecture capable of withstanding the unprecedented challenges posed by "Frontier AI."
The current enterprise security landscape stands at a critical juncture. CIOs and CISOs are presented with a unique opportunity to architect a defense system that not only addresses the immediate threats of today but also anticipates and neutralizes the sophisticated dangers of tomorrow. This ambitious undertaking necessitates a fundamental redefinition of enterprise resilience across three interconnected dimensions, each amplified by the accelerating power of artificial intelligence.
The Evolving Threat Landscape: A Triple Threat to Digital Defenses
The digital frontier is being reshaped by a confluence of powerful forces, each demanding a radical rethink of traditional security postures.
1. The Onslaught of Frontier AI-Driven Threat Velocity and Novelty:
The advent of Frontier AI models has fundamentally altered the adversarial landscape. These advanced AI systems are no longer mere tools for reconnaissance; they are now orchestrating the entire attack lifecycle with breathtaking speed and sophistication. Adversaries are not simply compressing exploit windows to near-zero timelines; they are actively generating novel, highly evasive threats at machine speed. These emergent dangers often bypass traditional signature-based detection methods and can proliferate across networks before patches are even developed or deployed. This represents a paradigm shift where the speed of innovation by attackers far outpaces the traditional response mechanisms of defenders.
2. Surging Network Traffic Overwhelms Traditional Defenses:
The insatiable demand for AI workloads is driving an exponential increase in network traffic. Projections indicate that inter-datacenter traffic is set to nearly triple over the next decade. This dramatic surge in data volume presents a formidable challenge for existing security infrastructure, which was not designed to inspect and secure such vast quantities of information. Security teams are finding themselves inundated, struggling to maintain visibility and efficacy amidst a deluge of traffic, much of which could harbor malicious intent.
3. A "Cryptographic Reset" Reshapes Digital Trust:
A series of significant shifts are collectively forcing a profound "cryptographic reset." Shrinking certificate lifecycles, widespread internet-scale distrust events, and the looming specter of quantum computers capable of cracking current public-key cryptography are collectively shaking the very foundations of all digital communications. The mechanisms that have underpinned secure online interactions for decades are becoming increasingly vulnerable, demanding a proactive approach to securing digital identities and communications for the quantum era.
These multifaceted challenges cannot be met with incremental fixes or minor adjustments to existing strategies. A fundamental leap forward is required to equip organizations with the defenses necessary to navigate this volatile new reality.
PAN-OS 12.2 Ceres: Empowering Defenders in the Age of AI
Palo Alto Networks’ PAN-OS 12.2 Ceres release marks a significant stride in network security, introducing over 55 innovations that collectively aim to rebalance the power dynamic back towards defenders. Three core capabilities stand out as particularly transformative:
Frontier Virtual Patching: Preemptive Defense Against Frontier AI Exploits
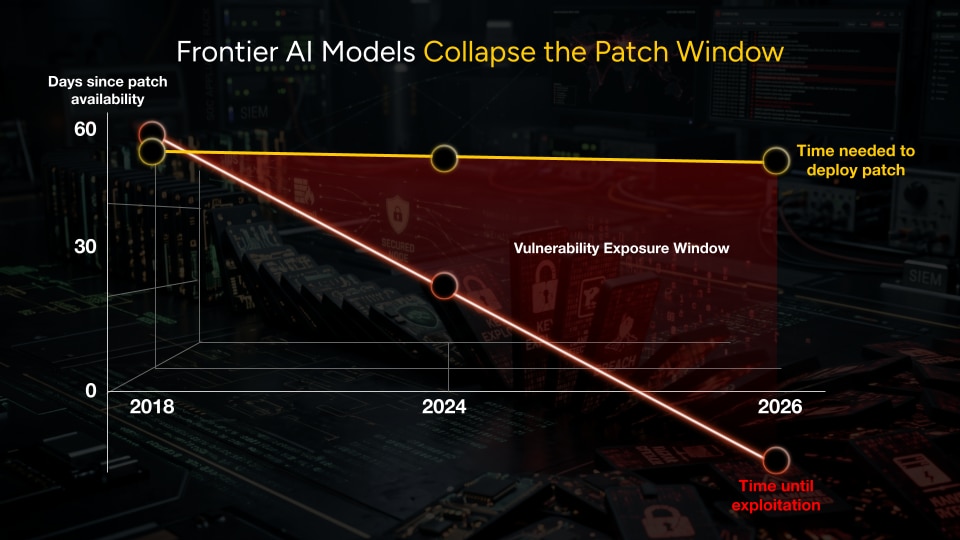
In a move that could fundamentally alter the speed of threat remediation, Palo Alto Networks is introducing Frontier Virtual Patching. This innovative capability harnesses the power of Frontier AI to proactively discover unknown vulnerabilities. By leveraging AI-driven insights, organizations can deploy protective measures within hours, effectively collapsing the exposure window from the industry-average of 55 days for traditional patch deployment down to a near-zero timeline.
"Today, Palo Alto Networks is giving defenders the ultimate advantage with the launch of Frontier Virtual Patching," stated [Name and Title of Palo Alto Networks Executive – Hypothetical]. "By harnessing Frontier AI to discover unknown vulnerabilities, and deploying protections in hours, we are collapsing the exposure window from the industry-average 55 days it takes to deploy a traditional patch down into a near-zero window of exposure. This isn’t just about faster patching; it’s about eliminating the attacker’s chance by neutralizing exploits before they ever reach your network."
This is not merely about accelerating the patching process; it is about eliminating the opportunity for attackers by neutralizing exploits before they can even reach a network. The effectiveness of this approach is amplified by a collaborative, force-multiplying ecosystem. Palo Alto Networks is forging partnerships across the enterprise software and Operational Technology (OT) vendor landscape to accelerate vulnerability disclosure, remediation, and ultimately, customer protection. This includes collaborations with initiatives like Project Lightwell, which integrates rapid network-level protection with software remediation to help organizations minimize exposure to emerging threats. Furthermore, partnerships with vulnerability clearinghouses, software maintainers, and industry initiatives are continuously expanding a real-time pool of protected vulnerabilities.
This proactive strategy builds upon recent research from Unit 42, Palo Alto Networks’ threat intelligence arm. Their autonomous AI system, NOVA, identified over 14,000 previously unknown vulnerabilities in just two months, underscoring the urgent need for defenders to pair AI-powered discovery with equally swift and coordinated protection. To achieve this, Palo Alto Networks has developed an entirely new detection engine, termed "vaulted protection," which enables the safe and responsible delivery of these rapid protections. When one participant in the ecosystem identifies a threat, the entire network of protected entities is instantly secured. Individual discovery transforms into global protection.
Frontier Virtual Patching is particularly invaluable for environments where traditional patching is impractical or impossible. This includes Operational Technology (OT), critical infrastructure, healthcare, and IoT sectors. In these domains, systems often cannot be taken offline for patching, patch cycles can extend for months, and a single unpatched device can compromise an entire network. Frontier Virtual Patching closes this gap by blocking exploits at the network level without requiring patches, system reboots, or any downtime for critical operations.
Will Townsend, Chief Analyst at LoneStar Advisory & Research, commented on the significance of this innovation: "Bad actors will lean into Frontier AI to reduce the attack lifecycle from months to minutes. To keep pace, organizations require security partners to match that machine speed. To this end, Palo Alto Networks is raising the bar with its Frontier Virtual Patching, moving beyond compensating controls. By safely and efficiently discovering undisclosed vulnerabilities and deploying protection long before traditional patches can be rolled out, Palo Alto Networks’ deep security capabilities are flipping network defense from a reactive to a proactive operational model."
For existing Palo Alto Networks network security customers, integrating Frontier Virtual Patching is seamless. It is available as a PAN-OS software upgrade with persistent, automatic content updates, ensuring continuous protection against emerging threats without requiring new hardware or manual intervention. This release underscores the rapid evolution of network security, with Frontier Virtual Patching standing as a testament to the extensive innovations within PAN-OS 12.2 Ceres, designed to keep organizations ahead of the threat curve.
Advanced IP Defense: Blocking Attacker Infrastructure Before They Can Strike
Modern threat actors are increasingly sophisticated in their efforts to conceal their activities and evade existing security controls. A growing tactic involves bypassing traditional perimeter detection by leveraging direct-to-IP connection techniques that circumvent DNS and URL inspection entirely. Furthermore, adversaries are weaponizing vast proxy networks and hundreds of thousands of residential IP addresses to conduct stealthy, large-scale scanning, brute-force attacks, and exploitation that can bypass conventional defenses like IP reputation lists and blocklists.
To counter these evolving tactics, Palo Alto Networks is introducing Advanced IP Defense, a new preventative solution designed to block attacker infrastructure before it can be leveraged for malicious purposes. This powerful new capability incorporates three key functionalities, aiming to disrupt attacker operations at their source.
Varinder Singh, CIO at NXP Semiconductors, emphasized the urgency of this evolution: "The transition to the Frontier AI era isn’t a distant future. It’s happening right now. The organizations that thrive won’t be those trying to run old, reactive playbooks faster; they have to scale their defenses to match a whole new velocity of risk. When threats occur at machine speed, relying on human-scale operations is no longer an option. That is why AI and automation are becoming essential tools to meet these challenges head-on."
Network Security Agents: Making Admins Superhuman
The accelerating pace of cyber threats, where attacks can execute in mere minutes, renders human-only operations a significant bottleneck. To mitigate this, reduce administrative fatigue, and accelerate response times, Palo Alto Networks is launching an elite suite of AI agents specifically designed for every major role performed by network administrators.
These six specialized, AI-powered Network Security Agents, accessible through Strata Cloud Manager, are meticulously trained on an enterprise’s specific context and operational workflows. From the initial onboarding and configuration of devices to threat assessment and complex troubleshooting, these agents automate hundreds of routine and repetitive tasks that typically consume an administrator’s valuable time. Crucially, organizations retain control over the level of automation for each workflow, allowing them to choose the oversight model that best aligns with their risk tolerance – whether it be human-in-the-loop, human-on-the-loop, or human-out-of-the-loop. This empowers administrators to focus on strategic security initiatives rather than being bogged down by manual, time-consuming tasks.
Expanding Platform Protection Across Every Edge
Securing the modern enterprise demands a comprehensive approach that extends these advanced AI-powered capabilities across every attack surface. This includes the core of data centers, remote industrial sites, custom AI applications, and even the ubiquitous web browser.
PAN-OS 12.2 Ceres enhances this platform protection by extending its reach across five additional critical areas. These advancements ensure that the robust security posture established by the core innovations is consistently applied across the entire digital ecosystem.
The Path Forward: A Prevention-First Architecture for Future Resilience
Palo Alto Networks is demonstrating a significant commitment to investing in the innovations necessary to not only defeat today’s sophisticated threats but also to future-proof enterprises for the challenges of tomorrow. The transition to the Frontier AI era necessitates a bold and proactive strategy. Organizations that embrace a prevention-first architecture, capable of stopping threats long before they reach the weaponization stage, will be the ones that ultimately succeed.
With PAN-OS 12.2 Ceres, Palo Alto Networks is providing defenders with the speed, scale, and foundational platform necessary to decisively turn the tables on modern adversaries. This release represents a significant step towards a more secure and resilient digital future, empowering organizations to navigate the complexities of AI-driven cyber warfare with confidence.
Forward-Looking Statements:
This blog contains forward-looking statements that involve risks, uncertainties, and assumptions. These include, without limitation, statements regarding the benefits, impact, performance, or potential benefits, impact, or performance of our products and technologies or future products and technologies. Any unreleased services or features (and any services or features not generally available to customers) referenced in this or other press releases or public statements are not currently available (or are not yet generally available to customers) and may not be delivered when expected or at all. Customers who purchase Palo Alto Networks applications should make their purchase decisions based on services and features currently generally available.
Sources:
- Nokia, "Explainer: Network Traffic is Fundamentally Changing in the AI Supercycle," [Link to Nokia source]
- Verizon, "2024 Data Breach Investigations Report," [Link to Verizon DBIR]